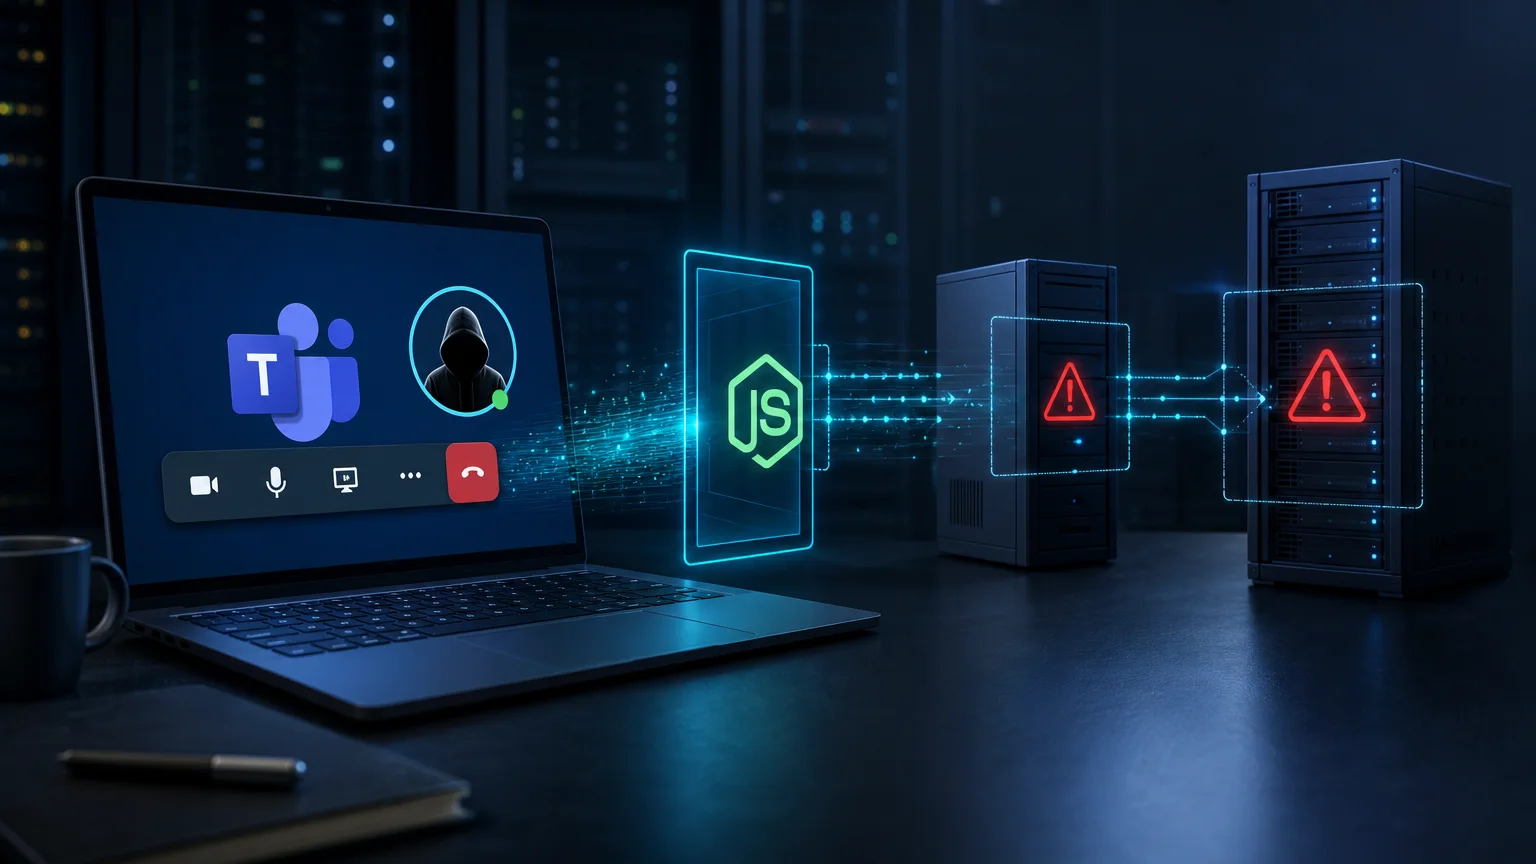
This campaign does not exploit a Microsoft Teams flaw. Attackers impersonate IT staff, persuade users to accept external support, and guide them to Quick Assist or similar tools, creating a route from a workstation to identity-critical systems.
How the attack chain develops
The operator may claim to handle a security or account update and ask the victim to bypass Teams warnings. An update-themed MSI is installed with msiexec; the payload can stage a portable Node.js runtime and encrypted JavaScript implant in the user’s writable application-data area.
Persistence may use an EdgeUpdate Run key or Startup shortcut. PowerShell, WScript, cmd.exe, Node.js, and rundll32.exe can blend activity with normal Windows execution, while HTTPS carries command-and-control traffic.
What defenders should investigate
- External Teams support contacts followed by Quick Assist or remote-management activity.
- PowerShell-driven MSI downloads and Node.js execution from user-writable paths.
- New Run-key or Startup-folder entries and concealed script-host activity.
- WinRM connections over TCP 5985 from unapproved management processes.
Why it matters
Operators can collect host, security-product, and virtualization details, capture screenshots, and query Active Directory for users, servers, and account descriptions. WinRM may reach file, database, and application servers, including domain controllers and certificate authorities.
Practical takeaway
Restrict external Teams collaboration and remote-support tools, verify helpdesk contacts, use phishing-resistant access controls, and limit WinRM to approved management systems. If a device may be affected, rotate accessible credentials and review its process tree, persistence locations, and outbound connections.